Optimize Your DORA Compliance with Secure, Efficient, and Future-Ready Solutions
Enhance your DORA management system with the fuentis Suite: streamlined implementation, automated monitoring, and continuous governance. Strengthen ICT risk management, reduce complexity, and stay fully audit-ready across all regulated financial operations.
- €0 entry plan for 12 months
- ISO 27001 · BSI IT-Grundschutz · TISAX · NIS2
- Made in Germany
Take the Next Step Toward Secure & Compliant Operations
Getting started is free: the free/Basic plan is €0 for 12 months.
Your Key Benefits
Why fuentis?
Made in Germany
GDPR-compliant, secure hosting in Germany and trusted by public authorities.
Easy & Efficient
Clear workflows and intuitive navigation – no steep learning curve, no tool overload.
Expert Guidance
Direct access to certified cybersecurity and compliance experts whenever needed.
Scales With You
From small teams to enterprise structures – modules and rights grow with your needs.
Standards Built-In
Supports ISO 27001, BSI IT-Grundschutz, SOC2, DSGVO and more out of the box.
Trusted by Leading Organizations
Get Started Now
Talk to our experts and discover how the fuentis Suite can simplify your security and compliance processes.
Getting started is free: the free/Basic plan is €0 for 12 months.
Frequently asked questions
What is DORA (Digital Operational Resilience Act)?
DORA is an EU regulation that has applied directly to banks, insurers, payment providers and other financial entities — plus their critical ICT third-party providers — since 17 January 2025. It harmonises requirements for ICT risk management, incident reporting, resilience testing and third-party risk management across the EU.
Who is affected by DORA?
Essentially the entire regulated EU financial sector: credit institutions, insurers, investment firms, payment and e-money institutions, crypto-asset service providers and other financial entities — plus the critical ICT third-party providers that supply them.
What software helps with DORA compliance?
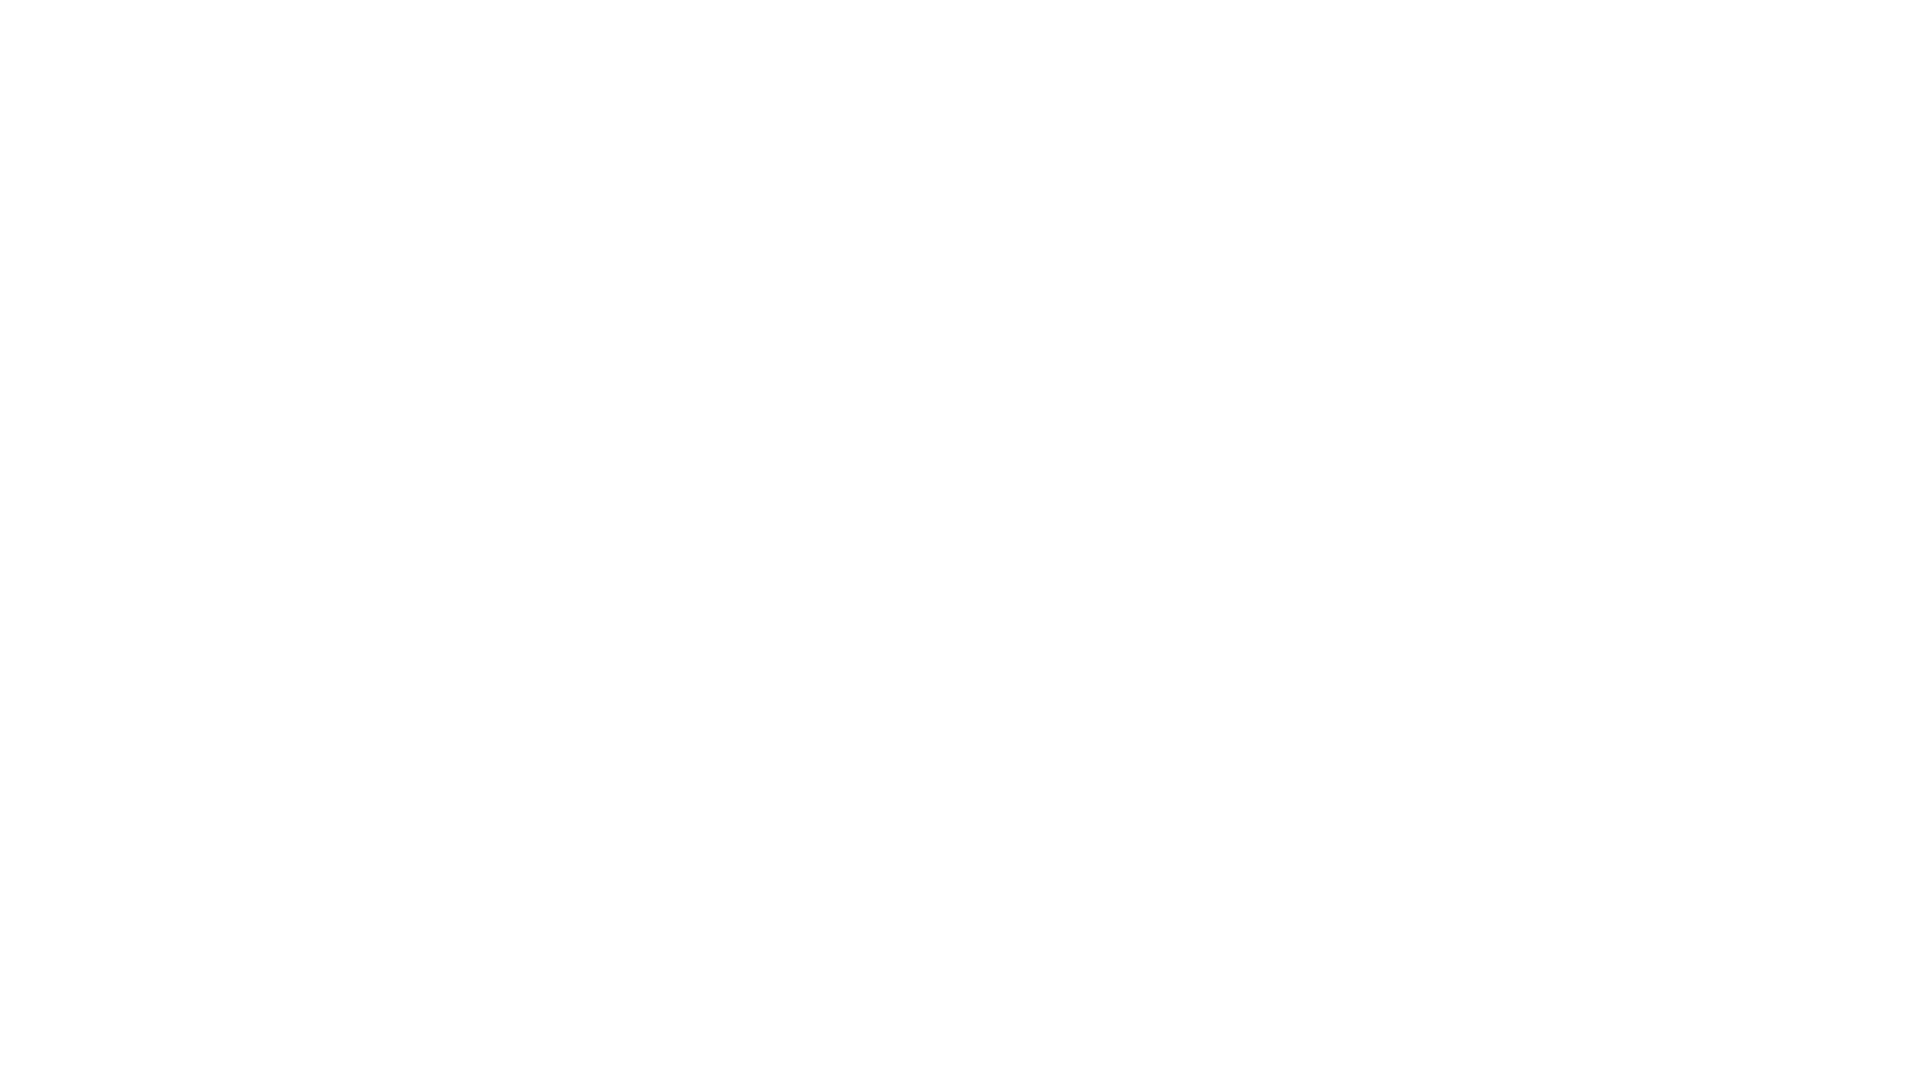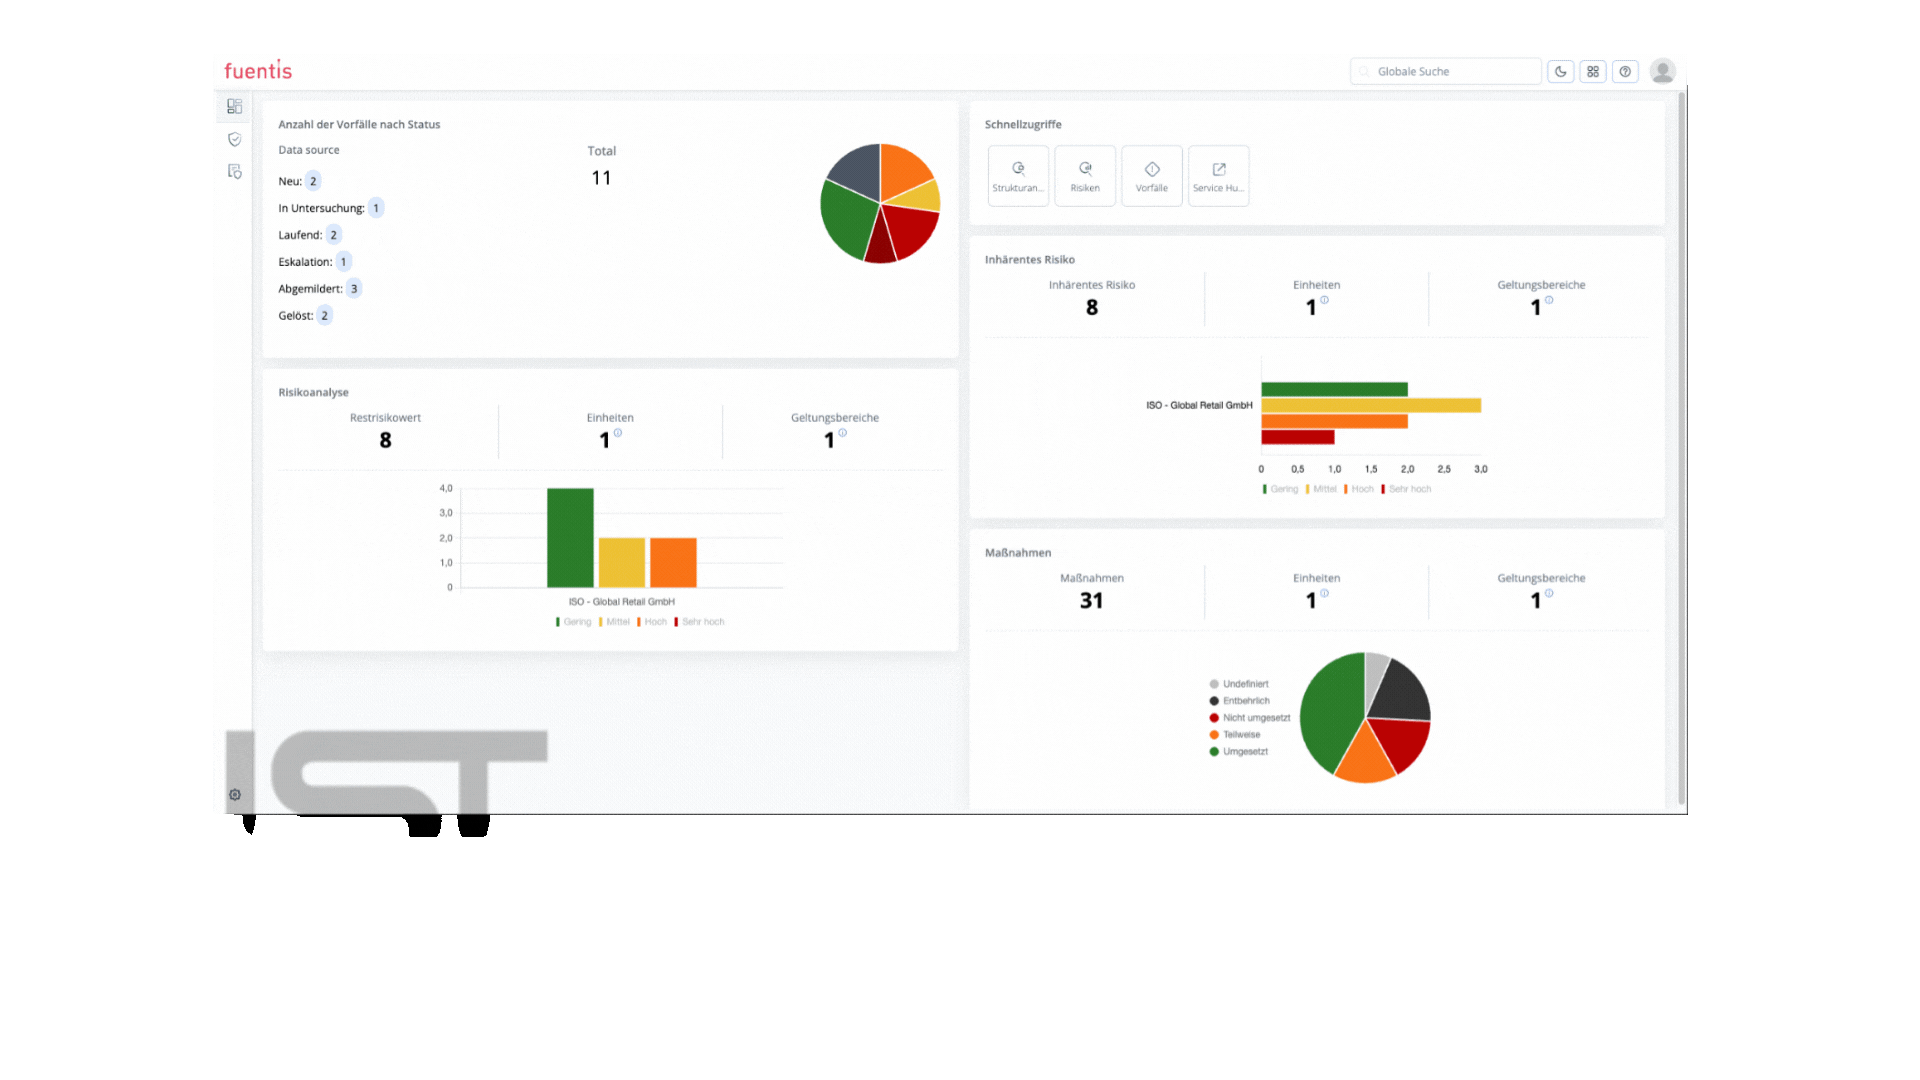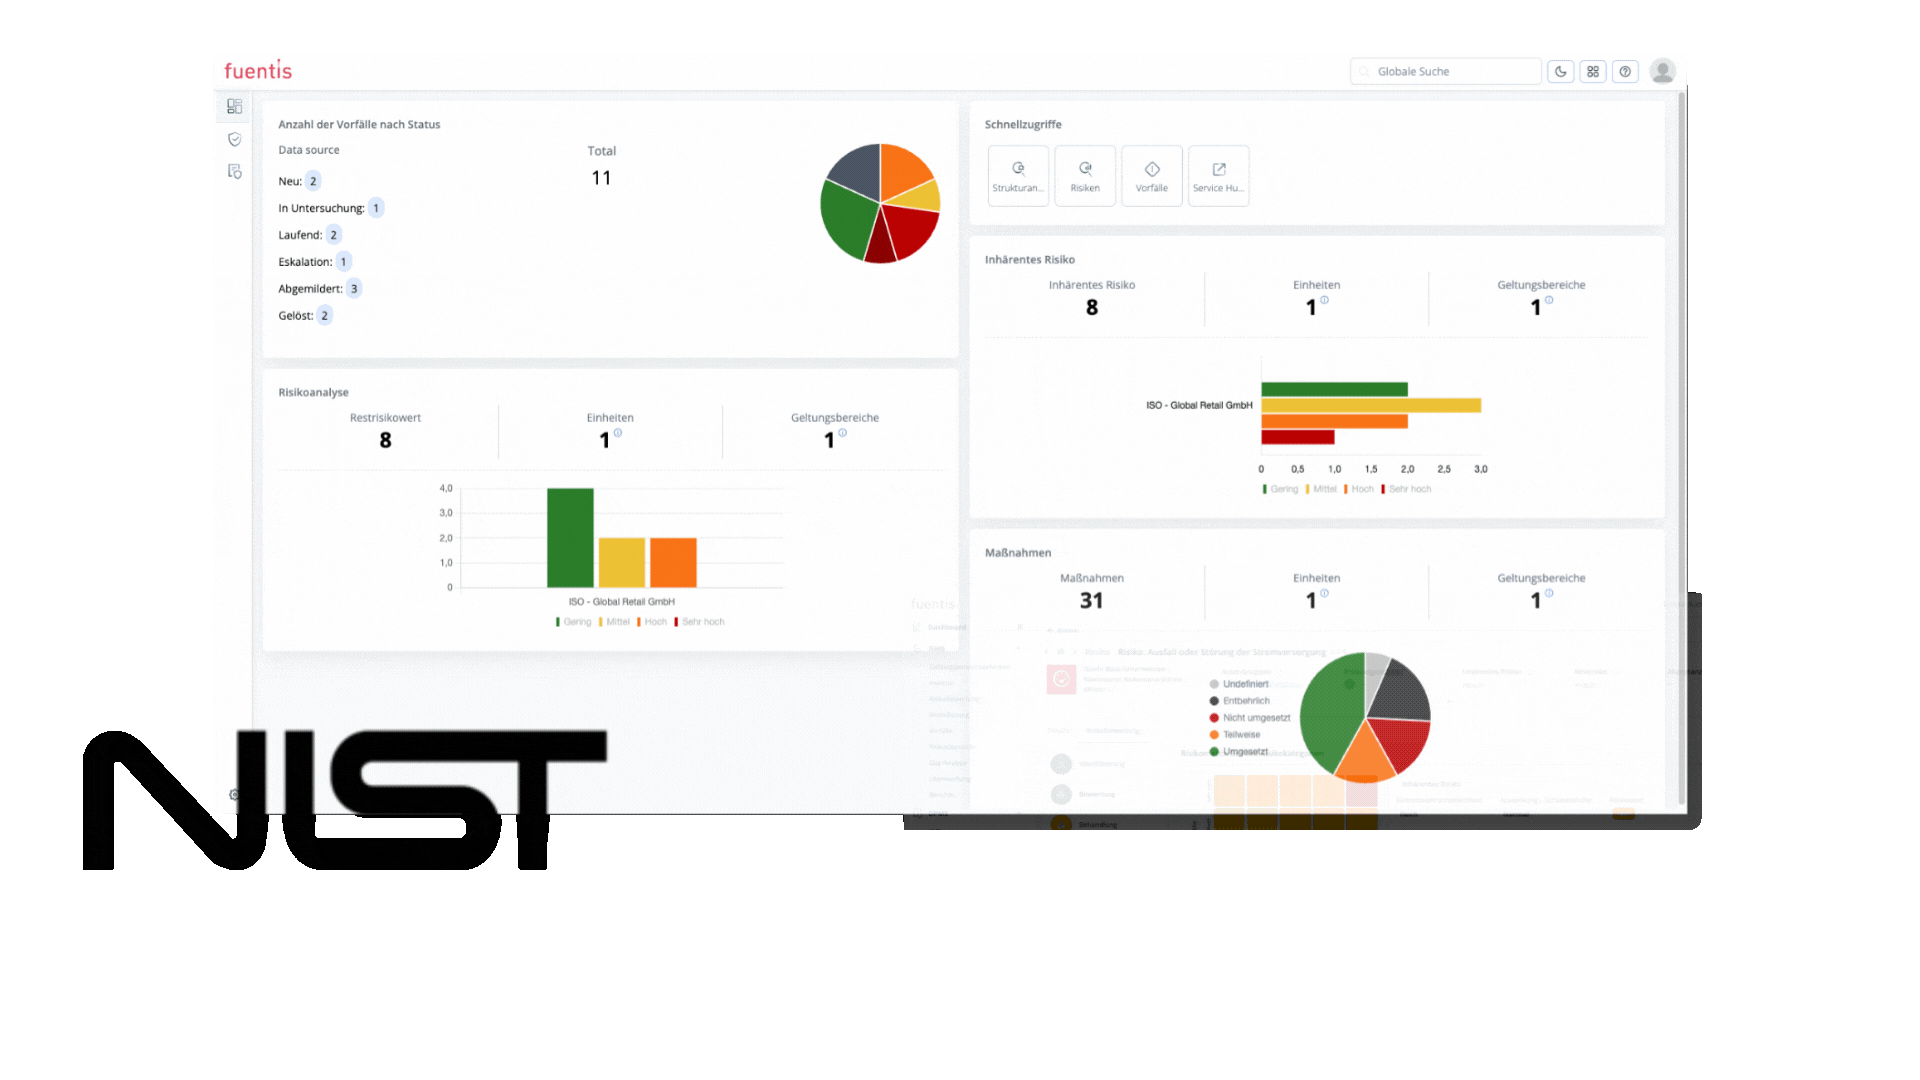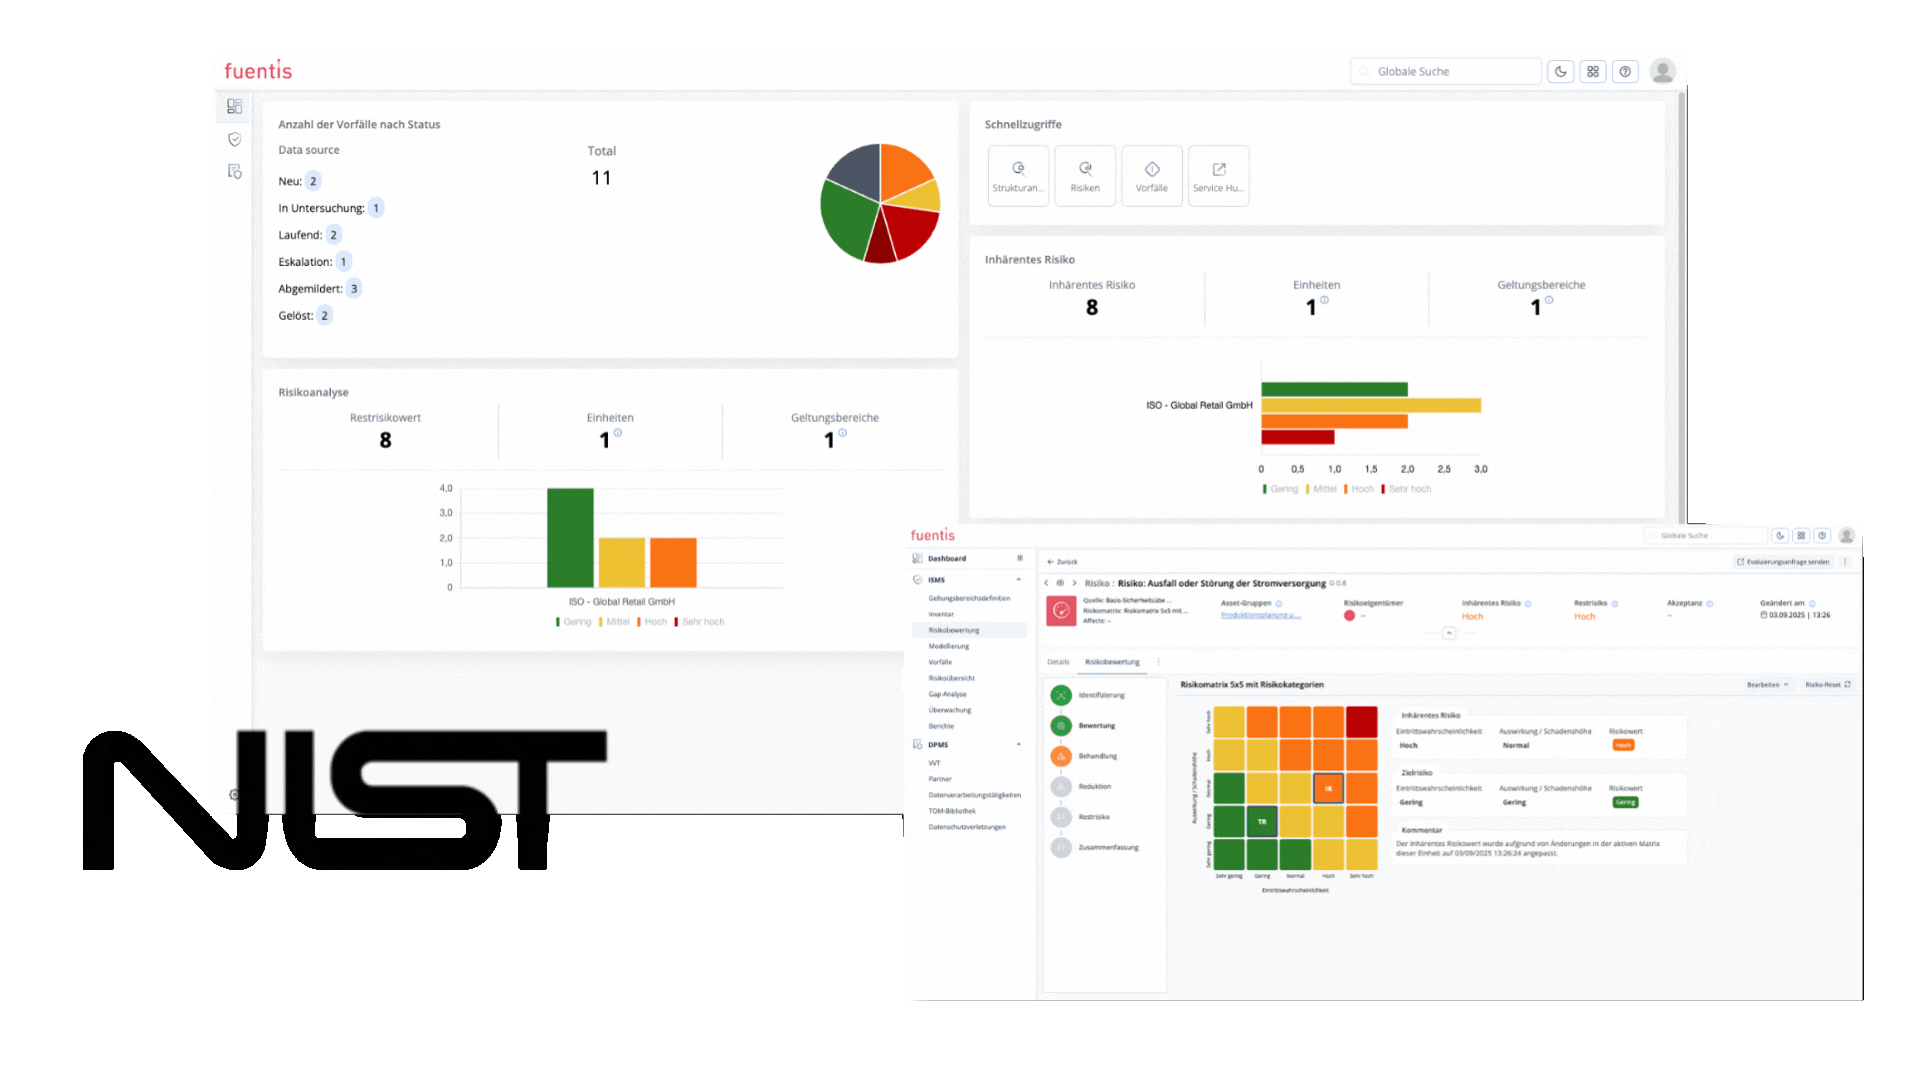
A GRC/ISMS platform such as the fuentis Suite covers the core DORA building blocks in one system: an ICT risk register, incident-reporting workflows, resilience testing management and third-party risk documentation — instead of scattered spreadsheets.
What was the DORA compliance deadline?
DORA has applied directly as an EU regulation since 17 January 2025. Unlike a directive, there was no separate national transposition deadline — affected entities were required to already meet the requirements by that date.